Agents & AI Engineering
AI engineering is making a model do the same correct thing twice: orchestration, evaluation, and the failure modes that appear once an agent has permissions. Heavy emphasis on security, because an agent that can act is an agent that can be exploited.
Latest in this section
Tools for this →
DeepSeek V4.1 Flash Changes the Economics of AI Agents
DeepSeek V4.1 Flash runs agent work for $0.15 in and $0.60 out per million tokens off-peak. What the benchmarks show and what it means for your costs.
Sep 11, 2026 · 10 min read

DeepSeek V4.1 Flash Pricing: What a Task Really Costs
DeepSeek V4.1 Flash pricing is $0.15/$0.60 per million tokens off-peak, and US business hours are off-peak. The per-task math, retries and review included.
Sep 11, 2026 · 6 min read

DeepSeek V4.1 Flash vs Opus 5: Where It Wins and Loses
DeepSeek V4.1 Flash vs Opus 5 and GPT-5.6 Sol on 19 vendor benchmarks: it wins older agent tests and trails the newest, hardest ones. The full table.
Sep 11, 2026 · 6 min read

Always-On AI Agents: Cheap Tokens Still Run Away
Always-on AI agents got cheap with DeepSeek V4.1 Flash, but cheap per token is not capped per month. How to run agents all day without an open-ended bill.
Sep 11, 2026 · 6 min read

Is DeepSeek V4.1 Flash Safe for Business Data?
DeepSeek V4.1 Flash data privacy: DeepSeek's privacy policy says it stores personal data in China. What open weights change, and four questions to ask first.
Sep 11, 2026 · 6 min read
Agentic AI Security: Securing Autonomous Agents
Agentic AI security means gating an agent's four attack surfaces — install, input, memory, and credentials — before you trust it in production.
Sep 1, 2026 · 7 min read
Prompt Injection: What It Is and How to Stop It
Prompt injection hides malicious instructions inside content an AI agent reads. Learn direct vs. indirect prompt injection and how to gate the kill-chain.
Sep 1, 2026 · 5 min read
MCP Security: How to Vet a Server Before You Install It
MCP security means grading a Model Context Protocol server or agent skill before you trust it. Here's what to check before you install — and why.
Sep 1, 2026 · 5 min read
Non-Human Identity Security: Securing AI Credentials
Non-human identity security means grading the API keys, tokens, and service accounts an AI agent runs on. Here's why NHI is the credential attack surface.
Sep 1, 2026 · 6 min read
AI Agent Memory Poisoning: The Silent Persistence Risk
AI agent memory poisoning writes false data into an agent's memory or RAG store so it's recalled as truth in every future session. Here's how it works.
Sep 1, 2026 · 5 min read
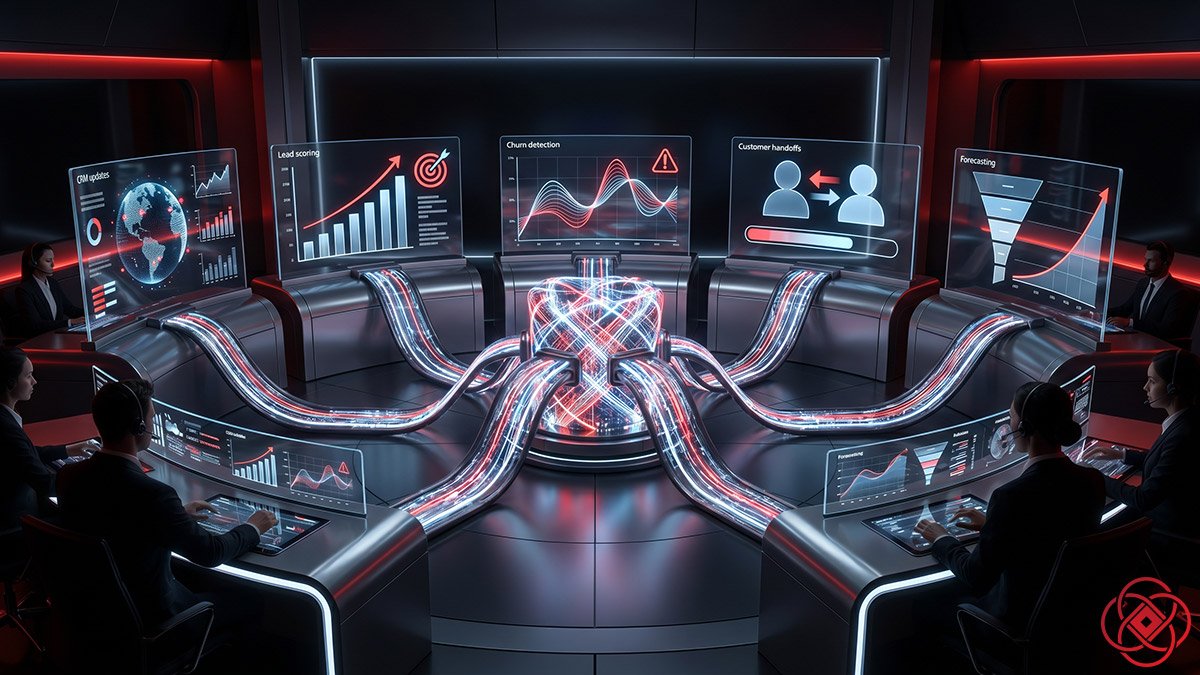
AI Workflows for B2B Teams: 5 to Run Now
AI workflows for B2B teams: run CRM updates, lead scoring, churn detection, handoffs, and forecasting to improve revenue execution.
Jul 8, 2026 · 12 min read
Claude Tag: AI Teammate or Trojan Horse?
Claude Tag brings AI into Slack as a shared teammate. Learn the upside, risks, governance issues, and why founders should own their context layer.
Jun 26, 2026 · 12 min read
Zero Trust for AI: Stop Deepfakes & Poisoned Data
Learn how zero trust for AI helps businesses defend against deepfakes, data poisoning, AI supply chain compromise, and over-permissioned agents.
Jun 22, 2026 · 9 min read
Autonomous SOC: AI Security Operations in 2026
Learn how to use an autonomous SOC AI security operations to replace manual triage, reduce alert fatigue, contain threats faster, and free analysts to hunt.
Jun 17, 2026 · 9 min read
Securing Agentic AI Insider Threats
Securing Agentic AI Insider Threats explains how AI agents become insider risks, how prompt injection spreads, and how to lock them down before damage.
Jun 15, 2026 · 9 min read
AI Security in 2026: Defense Framework
AI Security in 2026 means defending agentic systems, autonomous threats, AI agents, zero trust, AIBOMs, deepfakes, and machine-speed attacks.
Jun 11, 2026 · 8 min read
DeepSeek R4 for AI Agents: The Business Case
DeepSeek R4 for AI agents explained, including agent workflows, coding tasks, business automation, risks, and when to use it.
May 8, 2026 · 7 min read
Cloudflare Agent Stack for Production AI Agents
Cloudflare Agent Stack for Production AI Agents explains Mesh, Sandboxes, Workers, and model flexibility for secure enterprise AI deployment.
Apr 22, 2026 · 10 min read
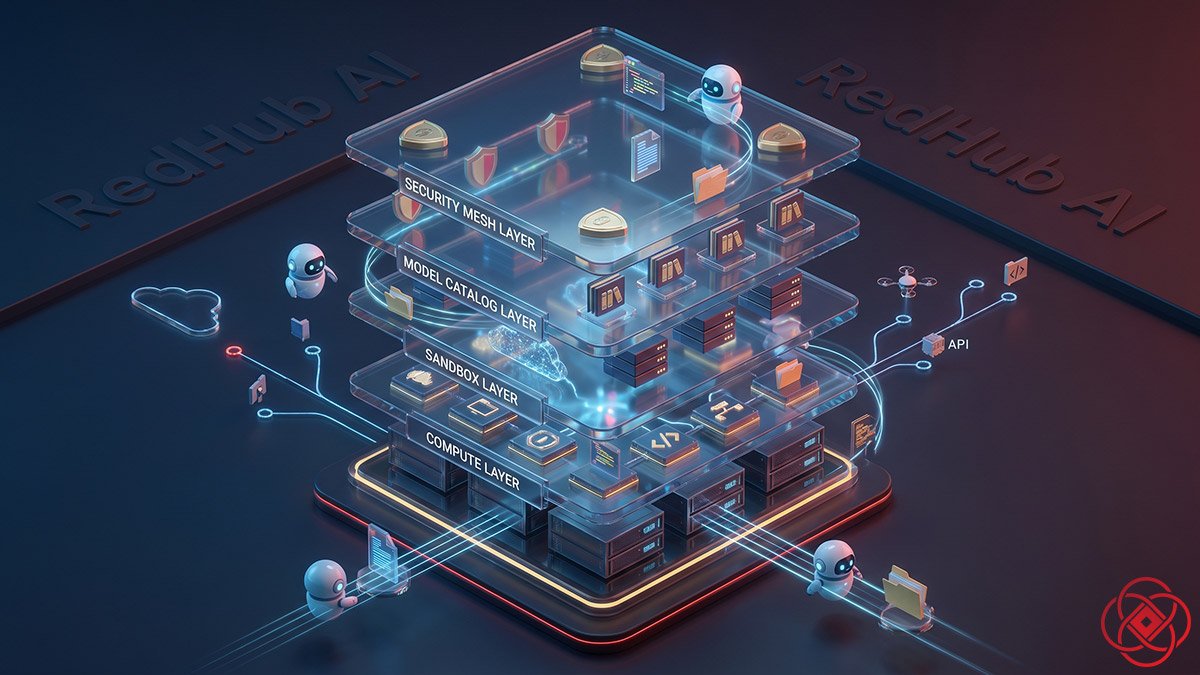
Cloudflare Agent Stack: Build Without Lock-In
Cloudflare Agent Stack helps founders build AI agents with model flexibility, Git-compatible storage, and less vendor lock-in.
Apr 20, 2026 · 8 min read
Cloudflare Sandboxes for AI Agents Explained
Cloudflare Sandboxes for AI Agents Explained: how persistent environments help AI agents run long tasks, retain context, and do real work.
Apr 17, 2026 · 7 min read
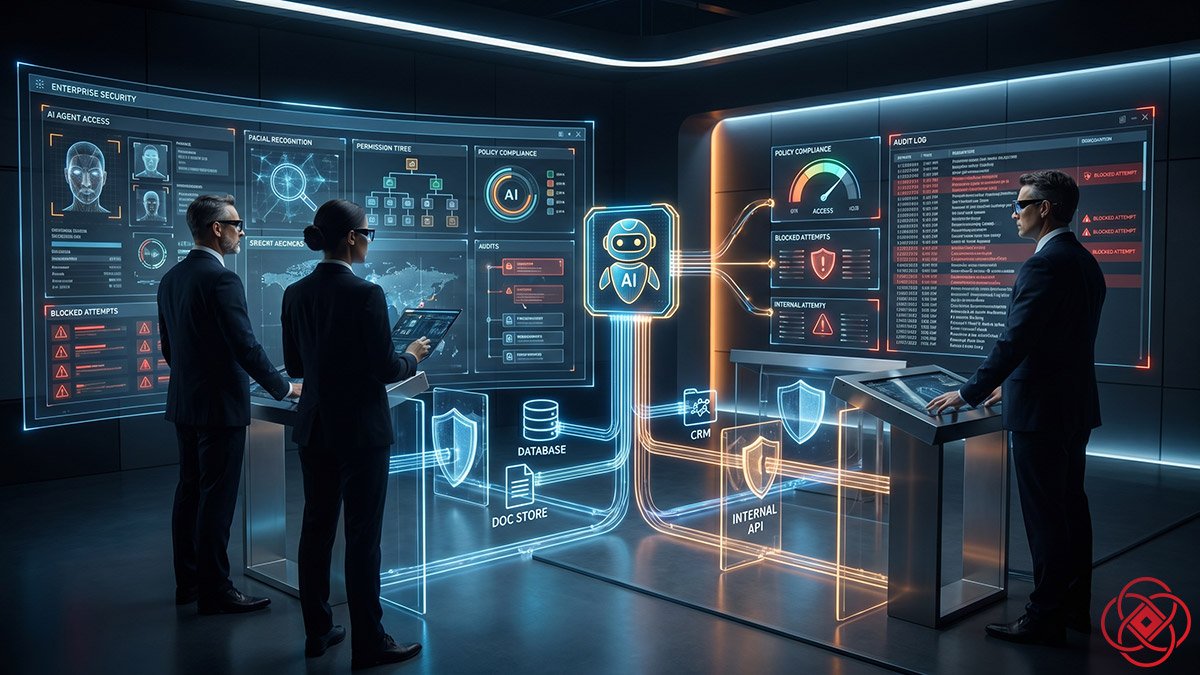
Cloudflare Mesh for Enterprise Security
Cloudflare Mesh for Enterprise Security gives AI agents secure identity-based access to private systems, APIs, and databases at enterprise scale.
Apr 17, 2026 · 7 min read
Cloudflare Dynamic Workers for AI Agents
Cloudflare Dynamic Workers for AI Agents change the economics of agent infrastructure with faster startup times, lower costs, and better scale.
Apr 16, 2026 · 7 min read
AI Agent Security Risks: Why Autonomous Agents Break Models
AI agent security risks explained. Learn how prompt injection, credential leaks, and continuous execution make autonomous agents vulnerable.
Feb 8, 2026 · 3 min read
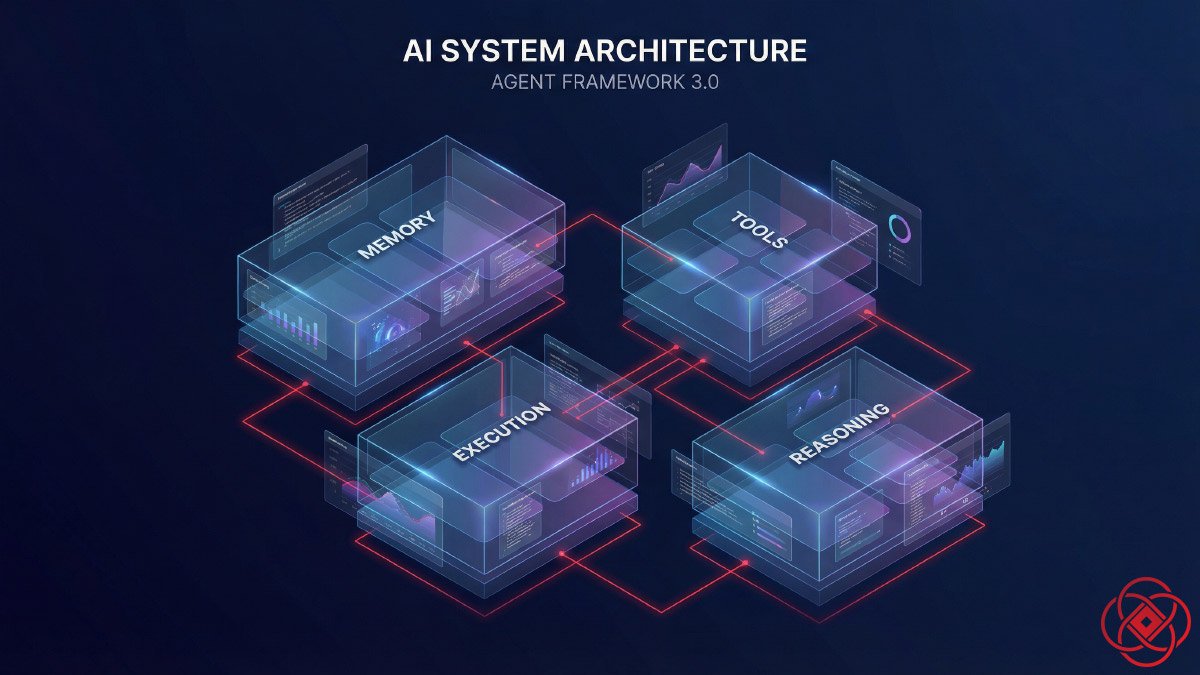
OpenClaw AI Agent Framework Explained
OpenClaw AI agent framework explained. Learn how this AI agent interprets goals, executes tools, uses memory, and runs autonomously without prompts.
Feb 6, 2026 · 3 min read